Social Browser Guide
Why Profile Isolation Matters for Modern Digital Workflows
Profile isolation is the practical foundation for safer accounts, cleaner testing, reliable automation, and organized team work.
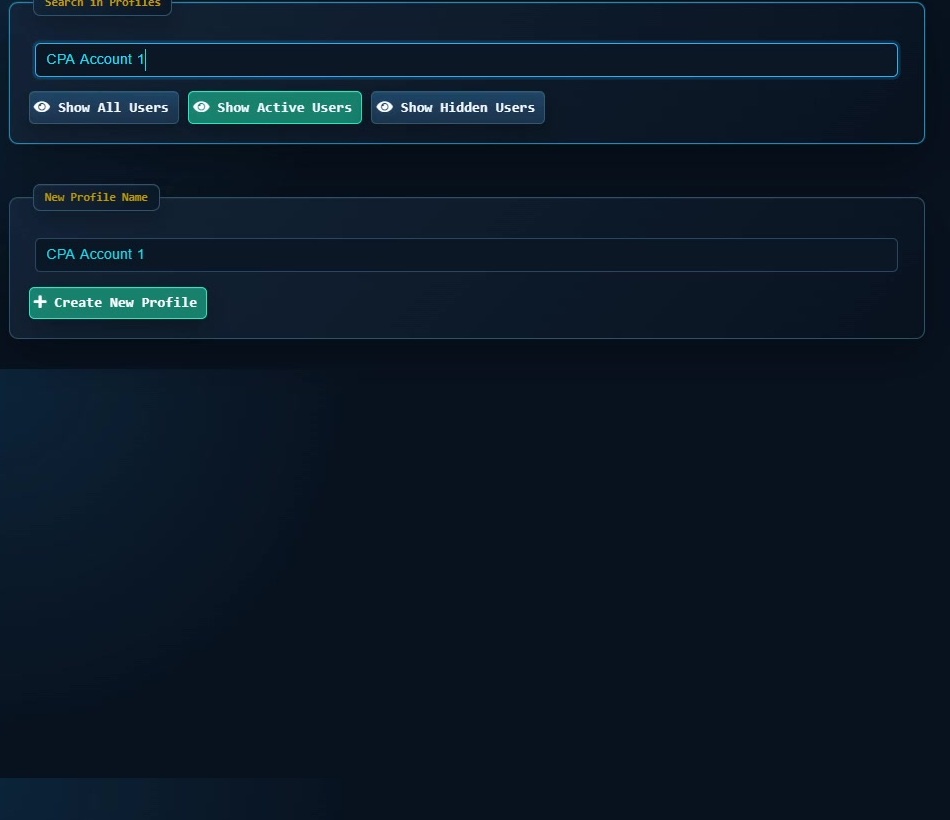

Profile isolation sounds like a technical detail until a team loses time to the wrong login, wrong cache, wrong extension, wrong proxy, or wrong account action. Modern digital workflows depend on many identities living on the same machine, sometimes in the same hour. The browser must protect those identities from blending together. Social Browser makes profile isolation a central principle instead of a hidden setting.
Profile isolation matters because digital work is no longer one person visiting one site from one stable account context. It is a chain of roles, accounts, permissions, regions, scripts, and team handoffs. The profile is the container that keeps those elements understandable.
What profile isolation should separate
- Cookies, local storage, cache, login sessions, and account history.
- Client, brand, region, project, and role based working contexts.
- Proxy settings, automation routines, and user scripts.
- Sensitive admin work from ordinary research and personal browsing.
- Active workflows from archived or experimental browser setups.
Isolation Problems And Practical Fixes
| Problem | Cause | Isolation practice | Benefit |
|---|---|---|---|
| Wrong account action | Shared login context | One profile per account role | Clear action boundary |
| Unstable testing | Mixed cache and storage | Test profiles by state | Repeatable results |
| Proxy confusion | Manual switching | Proxy bound to profile | Predictable network context |
| Script accidents | Script runs in broad scope | Script tied to profile purpose | Safer automation |
| Poor handoff | Context lives locally | Named profile groups | Team clarity |
Isolation Turns Identity Into A Container
Isolation Turns Identity Into A Container matters for one reason: account context on the web is made from many small signals, not just a username and password. A practical approach follows from that: a profile should contain the account, session history, storage, network expectations, and workflow notes that belong together.
Example: A seller account profile can be kept separate from a buyer account profile even when one worker needs to inspect both. Main risk: When account context pieces float freely, workers cannot easily know which signals are active. Payoff: The profile becomes a container that makes account context easier to understand.
Cookies And Storage Shape Behavior
The core issue is straightforward: web applications remember users through cookies, local storage, indexed data, cache, and other browser side records. One working rule follows from it: separating those records by profile prevents one workflow from inheriting assumptions created by another.
A representative case: A testing profile for a new user should not share storage with a profile used for a long time customer. What can go wrong: Mixed storage can make tests pass or fail for reasons nobody can reproduce. What good looks like: Clean profile state makes browser behavior more honest.
Isolation Reduces Cognitive Load
This section focuses on one operating fact: workers already track tasks, messages, metrics, deadlines, and decisions; they should not also track invisible browser state. The practical response is clear: profile names, groups, and visual organization can tell the worker what browser setup they are in before they act.
Example: A profile labeled with client, platform, and role gives a quick confirmation before a post or account update. Risk: When every window looks the same, the worker must carry too much risk in memory. Expected benefit: Isolation makes the safe action easier to choose.
Modern Teams Share Work, Not Just Passwords
A serious workflow includes context, status, access, history, and repeatable setup. One operating rule helps keep that boundary visible: isolated profiles can be assigned, documented, reviewed, and archived as work units.
One concrete example: A support team can maintain profile groups for open investigations, blocked cases, and completed reviews. Risk: Password sharing alone gives access without explaining the browser setup. Benefit: Profile isolation helps teams share the full shape of the work.
Automation Depends On Boundaries
For automation depends on boundaries, start from the problem itself: automation is more predictable when it knows exactly which browser setup it is controlling. Then make the working rule explicit: scripts should run inside profiles that match their purpose, account type, permissions, and expected page state.
In a real workflow: A script that prepares a report should live with the reporting profile rather than every profile a user opens. Watch for this failure mode: Automation without boundaries can act in the wrong context faster than a human would. Intended result: Isolated automation is easier to trust and easier to debug.
Network Context Belongs With Identity
Network Context Belongs With Identity matters for one reason: for many workflows, network settings are part of the account context browser setup rather than a separate technical detail. A practical approach follows from that: binding proxy configuration to a profile reduces manual switching and makes the expected network path visible.
Example: A region specific research profile can always open with the intended network context. Main risk: Manual network changes are easy to forget and hard to audit after the fact. Payoff: Profile based network context gives teams a more reliable place to manage the work.
Isolation Supports Safer Experimentation
The core issue is straightforward: teams need room to test scripts, settings, extensions, and account flows without disturbing active work. One working rule follows from it: experimental profiles can be separated from production profiles and retired when the test is finished.
A representative case: A developer can try a new user script in a sandbox profile before adding it to a profile used by the operations team. What can go wrong: Experiments inside active browser contexts leave behind state that later looks like a mystery bug. What good looks like: Isolated experiments encourage learning without contaminating daily work.
Compliance Starts With Visibility
This section focuses on one operating fact: teams cannot govern what they cannot see or name. The practical response is clear: profile isolation creates visible units that can be reviewed for purpose, ownership, access, and current status.
Example: An operations lead can ask why a profile exists, who uses it, and whether it should remain active. Risk: Unmanaged browser contexts make policy depend on informal habit. Expected benefit: Visible isolation gives review a practical starting point.
Isolation Makes Incidents Smaller
Mistakes still happen, but strong boundaries can limit how far they spread. One operating rule helps keep that boundary visible: when each account family or role lives in its own profile, an issue can be investigated inside a smaller scope.
One concrete example: If one profile has a bad setting or script, the team can inspect that browser setup without assuming every account is affected. Risk: A shared browser context makes incident review broad, slow, and uncertain. Benefit: Smaller boundaries make recovery calmer and more precise.
Isolation Is The Base Layer
For isolation is the base layer, start from the problem itself: many browser features are only useful after account boundaries are clear. Then make the working rule explicit: start with profile structure before adding automation, team handoffs, reporting routines, or complex account operations.
In a real workflow: A team that first defines profile groups by client and role can later add scripts and review processes with less confusion. Watch for this failure mode: Adding tools to an unstructured browser can make chaos more efficient instead of solving it. Intended result: Profile isolation gives every other workflow improvement a stable foundation.
Practical Next Step
A practical checkpoint for “Why Profile Isolation Matters for Modern Digital Workflows” is to validate one narrow case first: choose one Profile with one explicit account or role purpose. Confirm its session state stays separate, then add network settings, scripts, or extensions only when that Profile actually needs them.
Important Limits and Safe Use
A responsible implementation of “Why Profile Isolation Matters for Modern Digital Workflows” starts with this boundary: profile isolation reduces accidental state mixing, but it does not grant access to accounts or replace the rules of the services you use.
- Give each important Profile one clear purpose.
- Keep credentials and exported session data protected.
- Archive or remove obsolete Profiles so old access does not become hidden operational debt.
Expand “Why Profile Isolation Matters for Modern Digital Workflows” only after the expected result is repeatable, documented, and appropriate for the service being used.
Conclusion
The useful final test for “Why Profile Isolation Matters for Modern Digital Workflows” is whether the account state and purpose stay clearly separated from unrelated work.